HEOSSI · Singapore · Since 2020
Intelligence you can govern.Trust you can prove.
HEOSSI is a Singapore-incorporated deep-technology company building and operating a growing portfolio of governed solutions for environments where failure carries systemic consequence. Our work is designed for the 2030-2033 window - post-quantum and AI-governance deadlines the whole industry must now meet.
Capability matrix · live
Governed intelligence (AI)
BEE core; QNSI AI-security layer; SAAR makes no AI claim
Post-quantum crypto · FIPS 203/204/205
BEE via QNSI envelopes; SAAR attestation and licences live 21 Oct 2026
Real quantum hardware
BEE integrated, including the portal; SAAR via Fabric research; QNSI makes no hardware claim
Byte-exact recovery
SAAR recovery contract, verified before acceptance
87
PQC algorithms
13
Families
31
Workload classes
6
BEE tiers
In market now
Live product surfaces · 22 October 2026
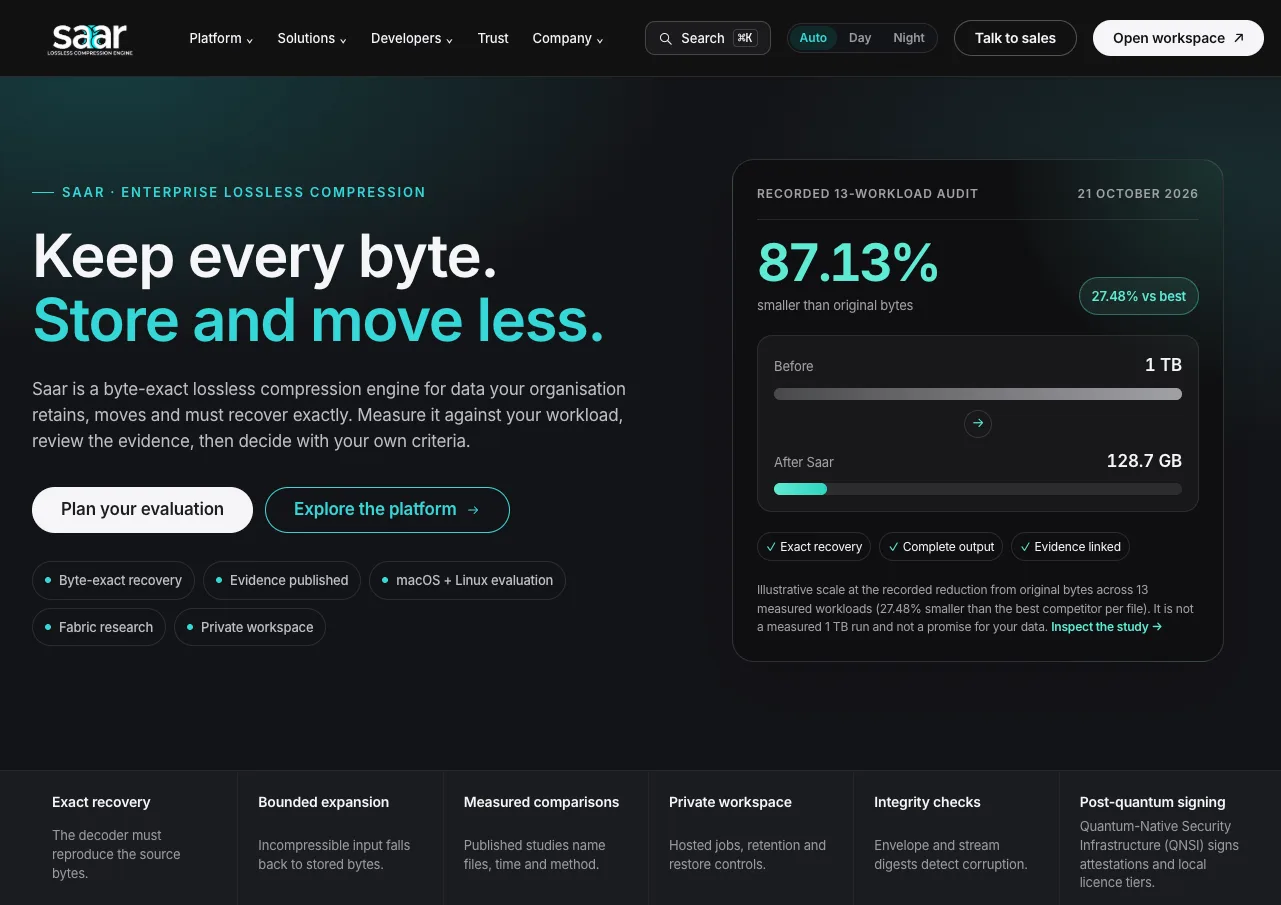
Portfolio status
Three solutions available.A wider portfolio beyond.
Three systems are in market today. The programs below show where HEOSSI is building next, in the domains where governed intelligence and provable trust carry consequence.
Explore the portfolioThe thesis
The next infrastructure layer is not software alone. It is trust, intelligence, and controlled execution.
HEOSSI develops the technology, governance and operating capability required to move deep-technology systems from research into controlled real-world use. The work began in July 2020, before the standards, the regulation and the agent market existed. Company-owned intellectual property, the internal XIIS control plane and a growing solution portfolio form a shared foundation for long-term development.
Why HEOSSI
Depth where it is hardest to build
Most platforms buy depth at the model layer or the perimeter. HEOSSI builds it in the governed layer between intelligence, cryptography and the systems that act on both. We build for the standards governments are still writing.
01
One control plane, three production systems
Most companies assemble their stack from other people's parts. HEOSSI builds its own control plane, XIIS, and operates it on its own AWS estate. It is the long-term foundation for how our systems are governed, evidenced and deployed.
02
Evidence before assertion
QNSI publishes reproducible conformance vectors. SAAR publishes per-workload recovery results and their limits. BEE publishes model lineage and release boundaries. And the founder publishes the methods themselves: two August 2026 arXiv papers on streaming guardrail equivalence and cross-implementation post-quantum conformance. Our claims are checkable by design.
03
Governed by construction
Autonomy is bounded, execution is replayable, and decisions carry provenance. Governance is architecturally enforced, not added as a reporting layer after deployment.
04
Built for consequence
Regulated finance, sovereign infrastructure, defence and industrial operations. We build for the environments where a silent failure is not an acceptable outcome.
Portfolio at a glance
Verifiable numbers, not adjectives
Each figure is drawn from a product-owned record or the published architecture. Every one links to its source so a buyer, auditor or investor can check it.
- 0
- Solutions available
- 0
- Post-quantum algorithms
- 0
- Measured workload classes
- 0
- XIIS control layers
BEE, QNSI and SAAR, each with published boundaries.
SourceAcross 13 families in QNSI, with reproducible conformance evidence.
SourceSAAR recovery results are published per sample, with method and limitations.
SourceThe internal control plane HEOSSI operates on its own AWS estate, in active development.
SourceEvidence in numbers
What the products actually measure
Charts are not decoration here. Each series is drawn from a product-owned record, and the source is named under every panel.
BEE
Intelligence ladder
66
Specialist domain families
1M
Token context
Source: Bee public facts contract.
QNSI
Post-quantum surface
Source: QNSI public contract via the solution catalogue.
SAAR
Recorded workload audit
Source: saar.heossi.com/facts.json, audit of 2026-10-21.
Portfolio
Available and in development
3
Available
10
Programmes
Source: solution registry and published architecture.
Where it applies
Built for environments where failure carries consequence
Governed intelligence, post-quantum trust and exact data recovery are only useful when they hold under regulation, audit and operational pressure.
01
Defense & Intelligence
Customer-controlled private or air-gapped deployments with offline signing, distributed edge routing, tamper-evident audit flows.
Sub-10s revocation capability (design target) and deterministic mission replay
Read the sector brief02
Regulated Finance
Quantum-safe document vaults, searchable encryption, automated retention and legal hold APIs with immediate regulator reporting.
PQC compliance with audit service webhooks
Read the sector brief03
Industrial Autonomy
Mission control for autonomous critical systems across aligned XIIS packs. XIIS expands through four horizontal packs - revenue, enterprise operations, technology, and research - plus seventeen industry and critical-infrastructure packs spanning satellite, defense, biotech, healthcare, agriculture, energy, nuclear, quantum, financial services, government and public sector, telecom and communications, transportation systems, marine, manufacturing, chemical and materials, water and wastewater, and emergency services.
<2% unplanned downtime target
Read the sector briefInvestor conversations
A portfolio built for the decade of governed systems.
HEOSSI is opening selected pre-seed conversations. Invest in the Singapore-incorporated global deep-technology company building and operating a growing portfolio of governed solutions for regulated, sovereign and mission-critical systems worldwide.
General information only. This is not a public offer or invitation to subscribe for securities. Any financing remains subject to fit, diligence, approvals, professional advice and definitive documentation.
- 3
- Solutions in market
- 87
- Post-quantum algorithms
- 1
- Internal control plane
- SG
- Singapore entity
BEE, QNSI and SAAR are available today, each with published boundaries.
QNSI ships a broad PQC surface with reproducible conformance evidence.
XIIS is the internal control plane HEOSSI operates on its own AWS estate.
HEOSSI (PTE.) LTD., UEN 202532790K, incorporated 28 July 2025.
Architecture
XIIS: HEOSSI's internal control plane
XIIS is HEOSSI's internal control plane, operated on the company's own AWS estate. It is an internal system today and is not currently integrated into BEE, QNSI or SAAR - a deliberate decoupling while the substrate matures, with re-integration staged as a portfolio programme; the six-layer model below describes the architecture it is designed against, where autonomy is bounded, replayable, deployable and visible.
Layer 01
Shared Foundation
Common contracts, durable persistence, and shared patterns that make the rest of XIIS composable.
- Shared contracts and schemas
- Persistence patterns and storage adapters
- Durable state handling
- Cross-platform package boundaries
Layer 02
Control and Trust
Governance, risk, identity, security, and QNSI-backed trust posture for bounded autonomy under audit.
- Identity and policy controls
- Governance and approval paths
- Risk scoring and release controls
- QNSI-backed trust and verification
- Security boundaries and runtime protection
Layer 03
Cognitive Substrate
Memory, context, knowledge, reasoning, and simulation systems that give XIIS bounded intelligence.
- Long-term memory and retrieval
- Context fusion and state modeling
- Knowledge systems
- Reasoning and confidence scoring
- Simulation and rehearsal
Layer 04
Execution Substrate
Inference, workflows, orchestration, tools, agents, and data fabric that turn intelligence into controlled action.
- Inference and model routing
- Workflow checkpoints and orchestration
- Agent and tool execution
- Data fabric and execution traces
- Replayable runtime behavior
Layer 05
Assurance and Observability
Telemetry, evaluation, grading, replay, and release validation to keep autonomous behavior measurable and auditable.
- Observability and runtime telemetry
- Evaluation and trace grading
- Failure analysis and replay
- Release validation gates
- Production-readiness assurance
Layer 06
Solution Consumption Surface
The SDK, MCP server/runtime, and domain packs that expose XIIS to the rest of the HEOSSI portfolio.
- Node SDK consumption
- MCP server and remote tool execution
- Cross-solution interoperability
- Domain-pack consumption model
Portfolio architecture
How the portfolio aligns to XIIS
XIIS is HEOSSI's internal control plane, operated internally today. BEE, QNSI and SAAR are offered publicly; the mapping below shows the architecture each entry is designed against, not current integration.
Solutions can align to multiple XIIS layers; the mapping shows primary architectural affinity, not exclusivity.
Available · Intelligence domain
Available · Trust domain
Available · Data domain
XIIS-native / closest to core
Control plane-aligned
Runtime and execution-aligned
Domain system-aligned
Fintech risk and intelligence
Industry system-aligned
This creates a coherent platform doctrine: XIIS is HEOSSI's internal control plane; the portfolio mapping shows architectural direction, not a claim of current integration.
The 2030-2033 window
The deadlines are already inside this decade.
The migration window is no longer a projection. Standards, national deadlines and AI regulation now converge on the same window, and the organisations that will operate in 2030 are restructuring for it now.
Reviewed 22 October 2026. Every entry links to its primary publication.
NIST finalizes the post-quantum standards
FIPS 203, 204 and 205 standardize ML-KEM, ML-DSA and SLH-DSA. NIST advises organisations to begin planning their migration to post-quantum cryptography now.
NIST, 13 Aug 2024HQC selected as a backup key-establishment standard
NIST selected HQC for standardization on 11 March 2025, adding a code-based alternative to ML-KEM. A draft standard is expected in 2026, with the final in 2027.
NIST, 11 Mar 2025US executive order sets 2030 and 2031 deadlines
Executive Order 14412, signed 22 June 2026, requires federal high-value and high-impact systems to move to post-quantum key establishment by 31 December 2030 and post-quantum signatures by 31 December 2031. Federal contractors are directed to comply by 2030.
The White House, 22 Jun 2026The EU AI Act becomes applicable
The Act applied from 2 August 2026. Transparency obligations are in force, high-risk obligations phase in to December 2027, and the AI Office enforces the rules for general-purpose models.
European Commission, 2 Aug 2026Singapore publishes agentic AI governance guidance
IMDA's framework provides technical and organisational guidance for responsible agent deployment, with humans retaining accountability for their systems.
IMDA, 22 Jan 2026AI infrastructure spending keeps climbing
Gartner forecast worldwide AI spending of $2.59 trillion in 2026, up 47% year over year, with infrastructure the largest spending segment.
Gartner, 19 May 2026Google and Cloudflare accelerate to 2029
Google set a 2029 post-quantum migration timeline, citing quantum hardware progress, error correction and revised factoring estimates. Cloudflare targets full post-quantum security, including authentication, in the same year, with more than two-thirds of browser traffic to its network already post-quantum protected.
Google, 25 Mar 2026; Cloudflare, Apr 2026Classical cryptography is deprecated, then disallowed
NIST guidance calls for RSA and elliptic-curve cryptography to be deprecated by 2030 and disallowed by 2035. US federal post-quantum key establishment is due by the end of 2030, with signatures due by 2031.
NIST, 2024; The White House, 2026Post-quantum signatures for US federal systems
The same executive order requires federal high-value and high-impact systems to complete post-quantum signature migration by 31 December 2031 - one year after key establishment.
The White House, 22 Jun 2026National-security systems complete CNSA 2.0
NSA's CNSA 2.0 timeline sets endpoints for national-security systems between 2030 and 2033, on a separate, classified track from federal civilian migration.
NSA, via Cloudflare, Jun 2026
Deployment architecture
Four deployment patterns, qualified per product
These are architectural patterns, not a statement that every HEOSSI solution supports every mode today. Current BEE, QNSI and SAAR documentation defines supported environments, service terms and qualification requirements.
01
Managed Cloud
Managed product access. Service levels, tenant isolation and supported regions depend on the product and service agreement.
- Multi-tenant isolation
- Managed infra
- Rapid deployment
02
Private VPC
A dedicated environment with customer-defined cloud boundaries, subject to product-specific qualification.
- Customer VPC
- Data residency
- Compliance control
03
Hybrid / Edge
An architecture pattern for split execution across cloud and on-premises or edge nodes. Supported components and connectivity require qualification.
- Split execution
- Edge runtime
- Unified control
04
Sovereign / Air-Gapped
An architecture pattern requiring qualification of disconnected operation, dependencies and key custody. Availability is agreed per product and engagement.
- Air-gapped
- Full isolation
- Offline signing
Expansion model
XIIS expands through horizontal packs and critical-infrastructure packs
XIIS is designed to expand through reusable operating planes and domain-specific pack deployments, not through isolated one-off applications.
These packs describe the aligned XIIS operating model and expansion logic, not equal priority launch commitments.
Horizontal packs
Shared operating planes that extend XIIS across commercial, operational, technical, and research execution.
Revenue
Coordinates growth, market intelligence, distribution, and commercial execution across the XIIS portfolio.
Demand generation, sales systems, partnerships, expansion, customer intelligence
Enterprise Operations
Extends XIIS into finance, compliance, workforce, procurement, and internal command systems.
Finance ops, compliance, procurement, workforce systems, internal governance
Technology
Applies XIIS to engineering, infrastructure, release control, platform operations, and developer execution.
Engineering, platform ops, cloud, data, release systems, developer intelligence
Research
Supports frontier R&D, simulation, experimentation, and high-consequence knowledge synthesis.
R&D workflows, experiment ops, simulation, discovery, technical intelligence
Industry and critical-infrastructure packs
Sector-specific pack deployments for regulated, sovereign, and mission-critical systems - applied as XIIS expands into each domain.
Company and product information
Who is HEOSSI?
HEOSSI (PTE.) LTD. is a Singapore-incorporated technology company, UEN 202532790K. Incorporated on 28 July 2025 as CUI LABS (PTE.) LTD., the company changed its name on 14 June 2026 while retaining the same legal entity and UEN.
Company identity and leadershipWhich HEOSSI solutions are available today?
BEE provides governed AI workspace and API access. QNSI provides post-quantum cryptography and security infrastructure. SAAR provides byte-exact lossless compression through a controlled technical evaluation. Further programmes are defined across intelligence, trust, industrial and financial domains and are advanced as capacity allows. They are not available to the public and no release dates are set.
Compare current solutions and development stagesCan I deploy a solution privately or air-gapped?
Deployment availability is product-specific. BEE Enclave supports qualified private, regulated and sovereign deployment paths; broader customer-operated and disconnected deployment is not generally available. QNSI offers a managed service, with private deployment subject to qualification. Architecture diagrams do not establish availability for every product or environment.
Review deployment requirements and product documentationIs HEOSSI certified against the standards it describes?
HEOSSI's compliance programme is planned; it does not represent independent certification, validation or conformity assessment as complete. Published QNSI software conformance evidence is distinct from certification of a deployed cryptographic module.
Read the assurance programme and scope boundariesNext step
Before your systems act, see them.
Explore HEOSSI's portfolio, technology, partnership pathways and company-level investor conversations.